Decentralized Sportsbooks and Hidden Threats: What Every US Bettor Must Know About Flash Loans, MEV, and Smart Contract Risk
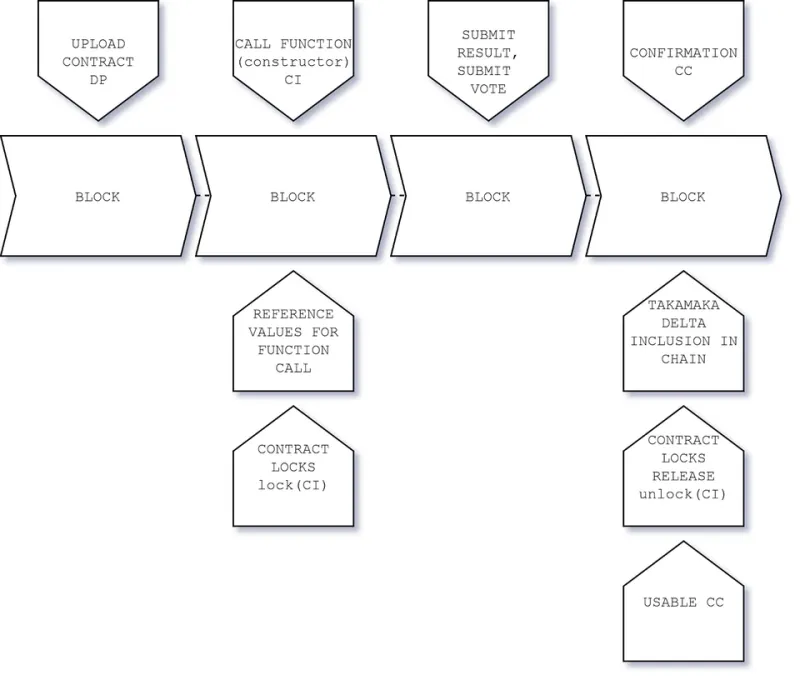
Photo: Giovanni AiliA, CC BY-SA 4.0, via Wikimedia Commons
The appeal of decentralized sportsbooks is genuine and well-documented. No intermediaries. No withdrawal limits enforced by a compliance department. No reliance on a company's solvency. For a growing segment of US crypto bettors, these features represent a meaningful upgrade over legacy platforms.
But the same architecture that removes centralized gatekeepers also removes centralized protections. When a traditional sportsbook gets hacked, there is typically a legal entity responsible for making users whole — or at least attempting to. When a decentralized protocol is exploited, the code executed exactly as written, and no one is liable for the outcome. Understanding the specific threat vectors that make decentralized betting platforms vulnerable is not a technical exercise reserved for developers. It is essential due diligence for any serious bettor.
What Is a Flash Loan Attack, and Why Should Bettors Care?
Flash loans are a mechanism unique to decentralized finance. They allow a borrower to access an essentially unlimited pool of capital — sometimes hundreds of millions of dollars — for the duration of a single blockchain transaction, provided the full amount is returned before the transaction closes. No collateral is required. No credit check. No waiting period.
In legitimate use cases, flash loans enable sophisticated arbitrage and collateral swaps. In the hands of an attacker, they become a tool for temporarily distorting market conditions in ways that exploit protocol logic.
For decentralized sportsbooks that rely on on-chain price feeds or liquidity pools to determine odds and settle bets, a flash loan attack can function as follows: an attacker borrows a massive sum, uses it to manipulate the price of a relevant asset or overwhelm a liquidity pool, triggers a favorable settlement condition within the betting protocol, collects the payout, and repays the flash loan — all within a single transaction block. The protocol behaved according to its rules. The attacker simply found a way to make those rules work against legitimate users.
Several DeFi protocols have suffered nine-figure losses through variations of this mechanism. Betting platforms that integrate with external price oracles or share liquidity infrastructure with broader DeFi ecosystems carry meaningful exposure to this class of attack.
MEV Sandwich Attacks: The Tax You Didn't Know You Were Paying
Maximum Extractable Value, commonly abbreviated as MEV, refers to the profit that can be captured by blockchain validators or sophisticated bots by reordering, inserting, or censoring transactions within a block before it is finalized.
A sandwich attack — one of the most common MEV strategies — works by detecting a pending transaction in the mempool (the queue of unconfirmed transactions visible to the network), front-running it with a buy order that moves the price, and then immediately selling after the victim's transaction executes at the inflated price. The victim effectively pays more than they should have, and the MEV bot pockets the difference.
In a betting context, this can manifest as degraded execution on any on-chain wager that involves token swaps or liquidity interactions. A bettor placing a large position on a decentralized platform may find that the effective odds they receive are materially worse than the odds they saw when initiating the transaction. The difference has been extracted by a bot operating faster than any human can respond.
This is not a hypothetical risk. MEV extraction has become a multi-billion-dollar industry on Ethereum and related chains. Bettors who do not account for it are, in effect, subsidizing sophisticated actors every time they interact with an on-chain market.
Smart Contract Vulnerabilities: Code Is Law Until It Isn't
The phrase "code is law" is a foundational principle of decentralized systems. It conveys that a smart contract will execute exactly as programmed, without exception. What it omits is the corollary: if the code contains a flaw, that flaw will also execute without exception.
Smart contract vulnerabilities come in several forms. Reentrancy bugs — the class of flaw that enabled the infamous DAO hack in 2016 — allow an attacker to repeatedly call a withdrawal function before the contract updates its internal balance, draining funds in a loop. Logic errors in bet settlement functions can allow users to claim winnings they did not earn, or prevent legitimate winners from withdrawing at all. Access control failures can give unauthorized parties the ability to modify odds, drain liquidity reserves, or pause the entire protocol.
The critical distinction for US bettors is between platforms that have undergone rigorous, third-party smart contract audits and those that have not. An audit does not guarantee safety — auditors are human and can miss issues — but an unaudited contract is a fundamentally different risk proposition than one that has been reviewed by multiple independent security firms.
How to Evaluate a Decentralized Sportsbook Before Depositing
Given these threat vectors, a systematic evaluation process is not optional for any bettor considering a decentralized platform. The following framework covers the most critical dimensions.
Audit history and transparency. A reputable decentralized sportsbook should be able to point to publicly available audit reports from recognized security firms. These reports should be recent — protocols that have undergone significant code changes since their last audit carry residual risk regardless of historical clean bills of health. Platforms that cannot or will not disclose audit documentation should be treated with significant skepticism.
Oracle infrastructure. How does the platform determine the outcome of events and the prices it uses for settlement? Platforms that rely on a single, centralized price feed are more vulnerable to manipulation than those using decentralized oracle networks with multiple independent data sources. Understanding the oracle design is essential to assessing flash loan and price manipulation risk.
On-chain activity and liquidity depth. Shallow liquidity pools are more susceptible to manipulation and create worse execution conditions for large bettors. Reviewing on-chain data to assess actual liquidity depth — not just advertised figures — provides a realistic picture of execution quality and resilience.
Bug bounty programs. Mature protocols typically maintain active bug bounty programs that incentivize white-hat security researchers to identify and disclose vulnerabilities before malicious actors exploit them. The existence and generosity of a bug bounty is a meaningful signal of a platform's security culture.
Insurance and coverage mechanisms. Some DeFi ecosystems have developed protocol-level insurance products that can compensate users in the event of a smart contract exploit. While coverage is never guaranteed and often limited, the availability of such mechanisms represents a meaningful layer of protection absent from uninsured alternatives.
Red Flags That Should Give Any Bettor Pause
Not all risk indicators require deep technical knowledge to identify. Several red flags are accessible to any bettor willing to look.
Anonymous development teams with no verifiable track record represent elevated counterparty risk. Platforms that have launched without public audits and justify this by citing the cost or pace of development are signaling that security is not a priority. Unusually high advertised yields on liquidity provision — the kind that seem too good to be justified by legitimate betting volume — often indicate unsustainable tokenomics that benefit early insiders at the expense of later participants.
Social media activity that emphasizes price speculation over product development, or communities that aggressively suppress questions about security practices, are cultural indicators worth taking seriously.
Choosing Platforms That Take Security Seriously
The decentralized betting space is not uniformly risky. There are platforms that have invested heavily in security infrastructure, maintained transparent audit trails, and built track records over multiple market cycles without a significant exploit. The gap in security posture between the best and worst actors in this space is substantial.
For US bettors evaluating their options, the combination of a reputable platform with strong security credentials and the kind of professional account infrastructure available through Hello88 Pro — where cryptocurrency integration is paired with institutional-grade operational standards — represents a meaningfully safer foundation than chasing yield on an unvetted protocol.
Decentralized finance has introduced genuine innovations in how bets are placed, settled, and managed. But innovation without security diligence is simply risk dressed in a new interface. The bettors who thrive in this environment are the ones who treat security evaluation as seriously as they treat odds analysis — because in the long run, protecting your capital is the prerequisite for everything else.